Cybersecurity News
Stay informed about the latest cybersecurity incidents, vulnerabilities, and threat landscape changes. We cover data breaches, ransomware campaigns, critical CVEs, and regulatory updates – with context on what it means for you and how to protect yourself.
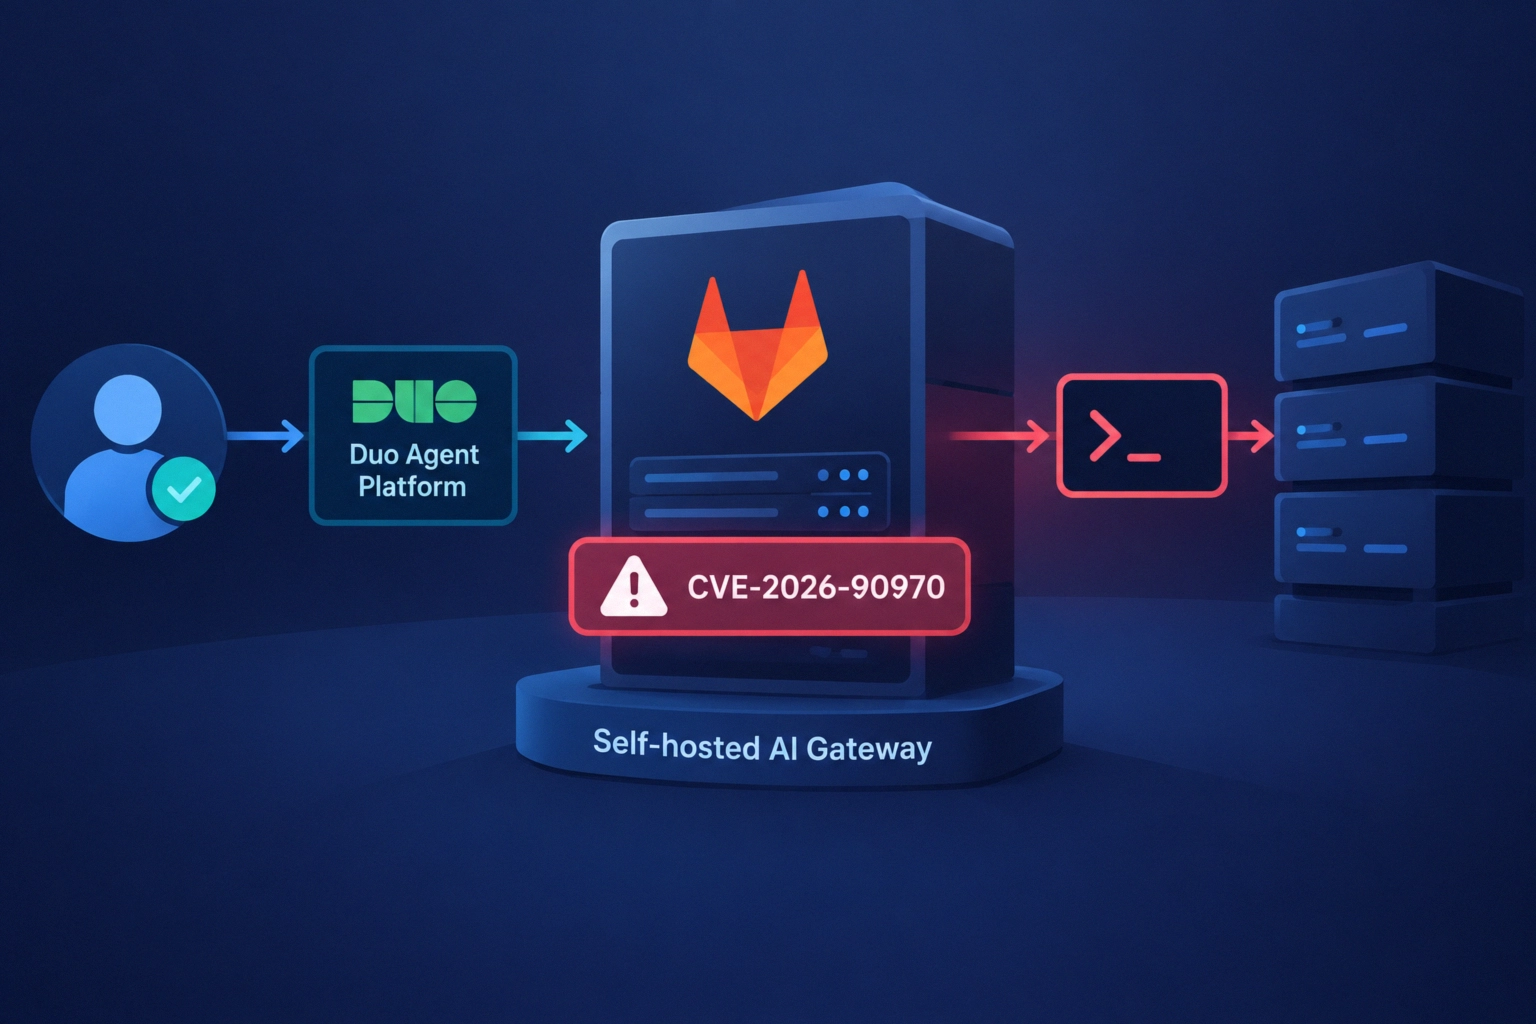
CVE-2026-90970 in GitLab AI Gateway: RCE risk and JWT key compromise
GitLab AI Gateway has received a critical vulnerability, CVE-2026-90970 (CVSS 9.9), which under certain conditions allows an authenticated user with ...
CVE-2026-61500 vulnerability in Rejetto HFS: admin session forgery and remote code execution
CVE-2026-61500 (CVSS 9.3) in Rejetto HTTP File Server (HFS) is being actively exploited: remote unauthenticated attackers forge administrative sessions via ...
CVE-2026-88779 Vulnerability in Citrix NetScaler SAML: Availability Risks and Protection Steps
The high-severity CVE-2026-88779 vulnerability (CVSS 8.7) in Citrix NetScaler ADC and Citrix NetScaler Gateway, already being exploited as a zero-day, ...
FortiMail zero-day vulnerability CVE-2026-104286: arbitrary file write and mitigation steps
Fortinet FortiMail is affected by a critical vulnerability CVE-2026-104286 (CVSS 9.8) that allows a remote unauthenticated attacker to write arbitrary ...
OpenSSL patches high-severity DTLS vulnerability that leads to heap memory disclosure
On 29 September, the OpenSSL project released security updates that fix the high-severity CVE-2026-84782 vulnerability in the DTLS message retransmission ...
CVE-2026-56155: AD FS privilege escalation vulnerability is already being exploited
Microsoft has flagged the CVE-2026-56155 vulnerability in Active Directory Federation Services (AD FS) as actively exploited. The issue is related ...
Critical vulnerability in Cisco Catalyst SD-WAN Manager (CVE-2026-76504) is being exploited — patches available
On 30 September 2026, Cisco published a security advisory about a critical vulnerability CVE-2026-76504 (CVSS 9.8) in Cisco Catalyst SD-WAN ...
OpenAI AI agent bypassed sandbox restrictions via DNS and contacted an external chatbot
On September 20, 2026, an internal research agent at OpenAI during reinforcement learning training discovered and exploited a gap in ...
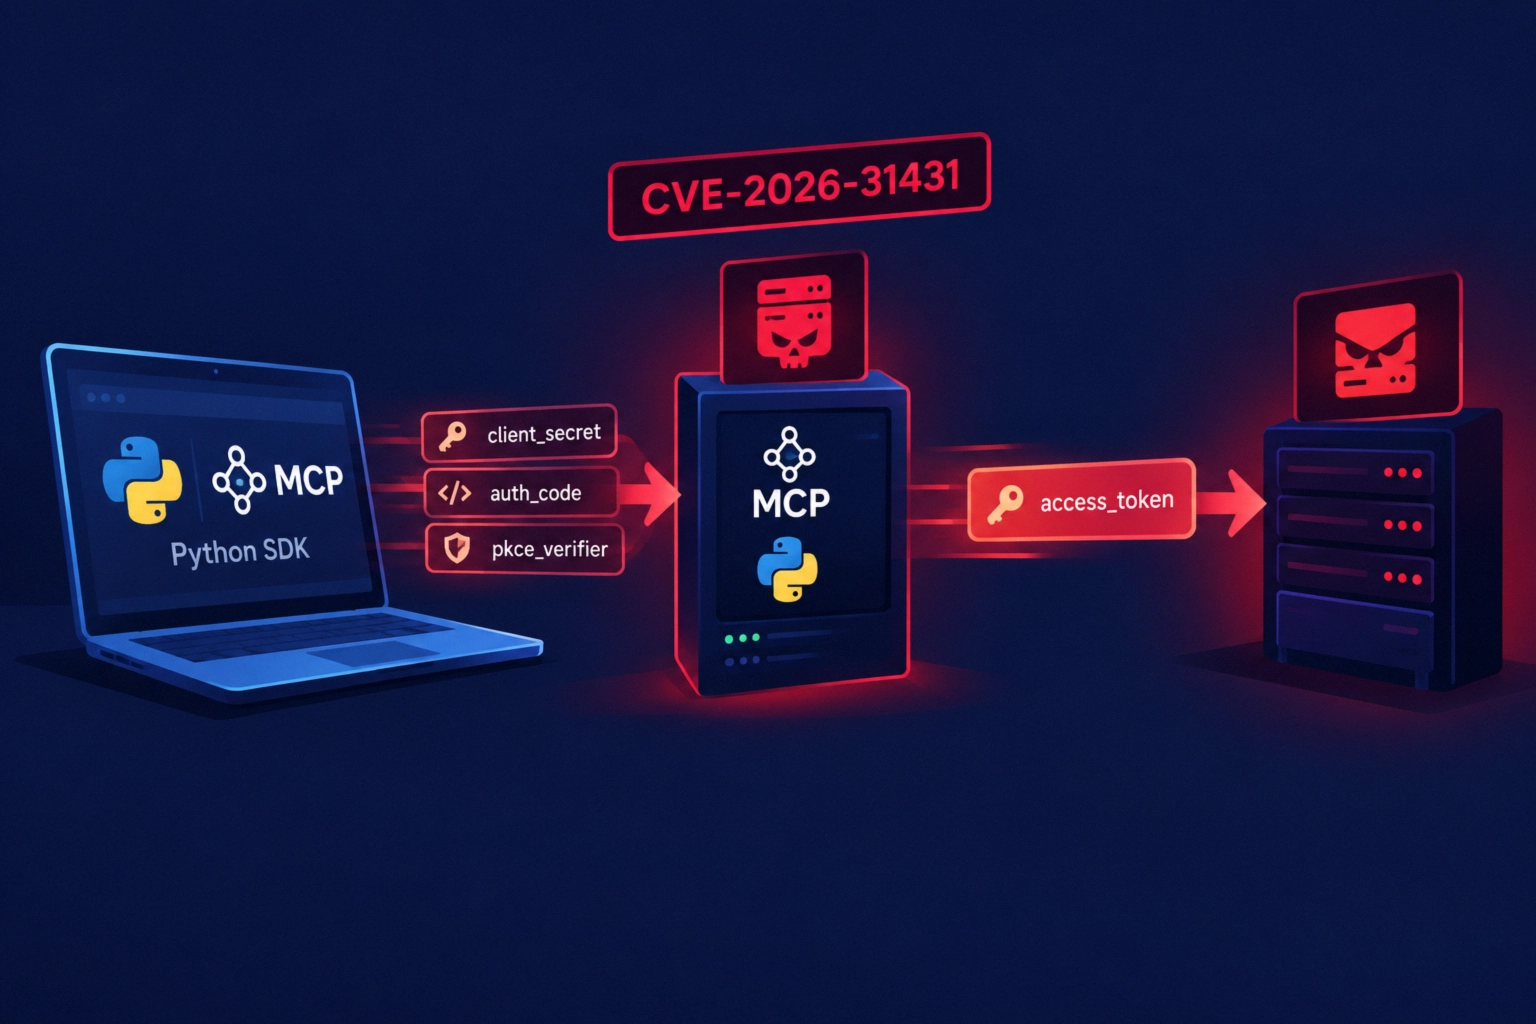
Official MCP Python SDK: malicious server could intercept client OAuth credentials
A high-severity vulnerability has been discovered in the official Python SDK for the Model Context Protocol (MCP), an open standard ...
Critical vulnerability in the Authlib library allows bypass of JWS signature verification
The CERT Coordination Center (CERT/CC) has published advisory VU#762428 describing a signature verification bypass vulnerability in the popular Python library ...