Cybersecurity News
Stay informed about the latest cybersecurity incidents, vulnerabilities, and threat landscape changes. We cover data breaches, ransomware campaigns, critical CVEs, and regulatory updates – with context on what it means for you and how to protect yourself.
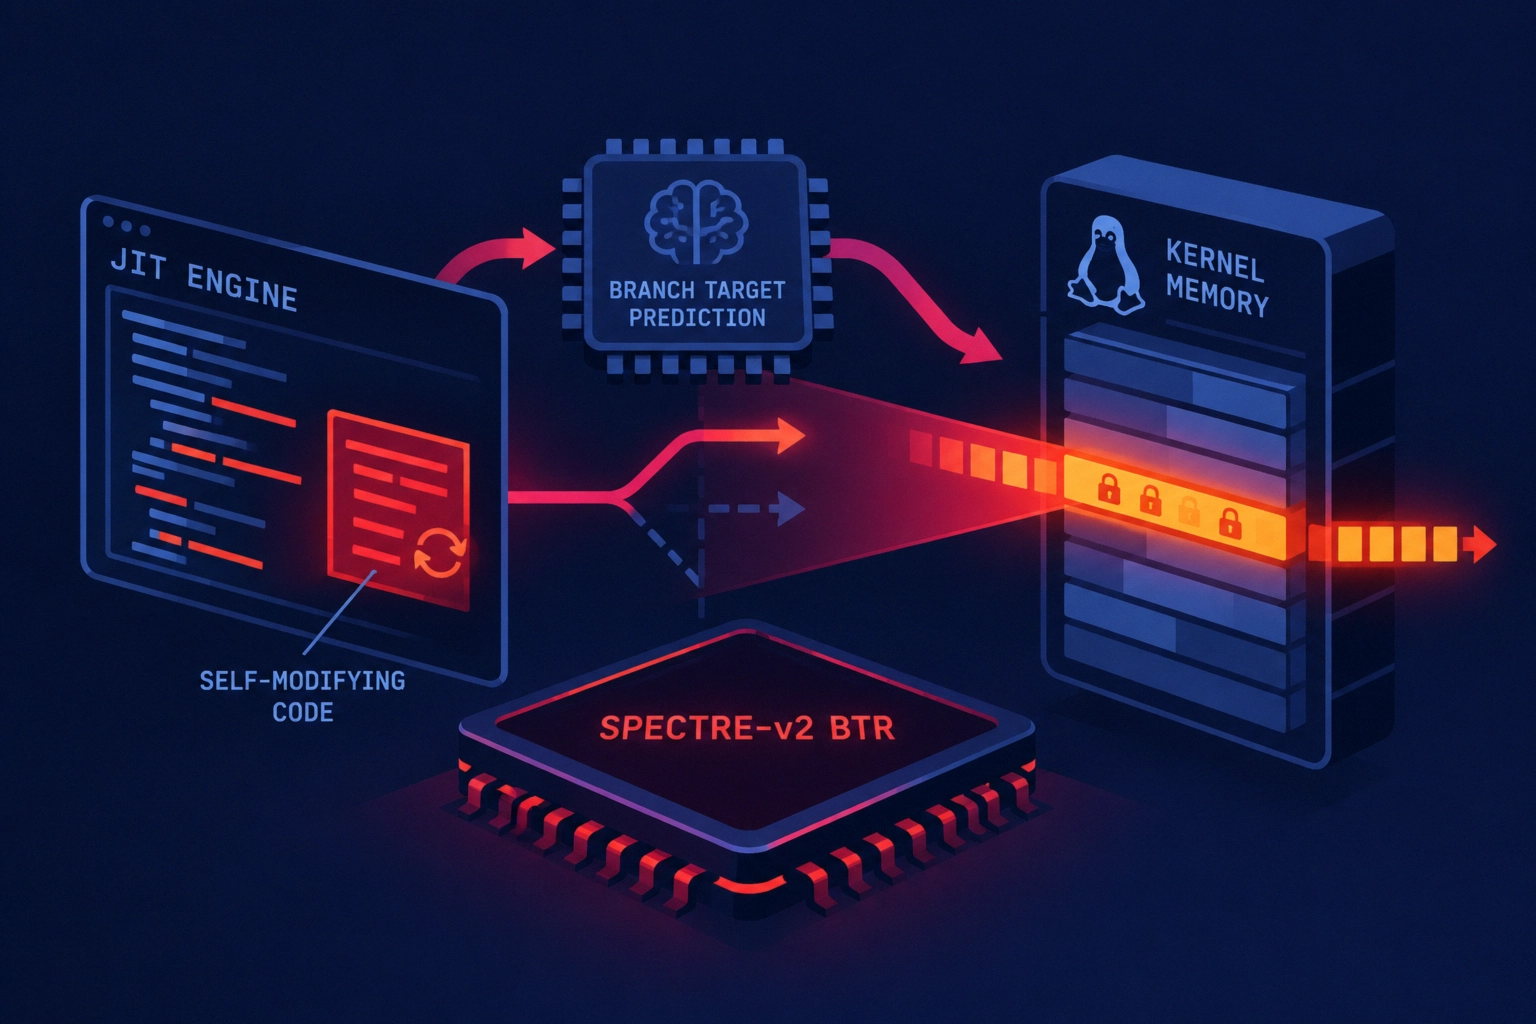
Branch Target Reuse — a new Spectre-v2 variant that bypasses existing Linux kernel protections
Researchers from VUSec and Scuola Superiore Sant’Anna have disclosed a new Spectre-v2 attack variant called Branch Target Reuse (BTR). The ...
Apple fixes CoreGraphics vulnerability reportedly used in targeted attacks
On September 28, 2026, Apple released security updates for iOS, iPadOS, and macOS that fix the CVE-2026-86950 vulnerability in the ...
SharePoint and MikroTik RouterOS: CISA confirms active exploitation of three vulnerabilities
On 25 September 2026, CISA added two vulnerabilities to the Known Exploited Vulnerabilities catalog — CVE-2026-65660 in Microsoft SharePoint and ...
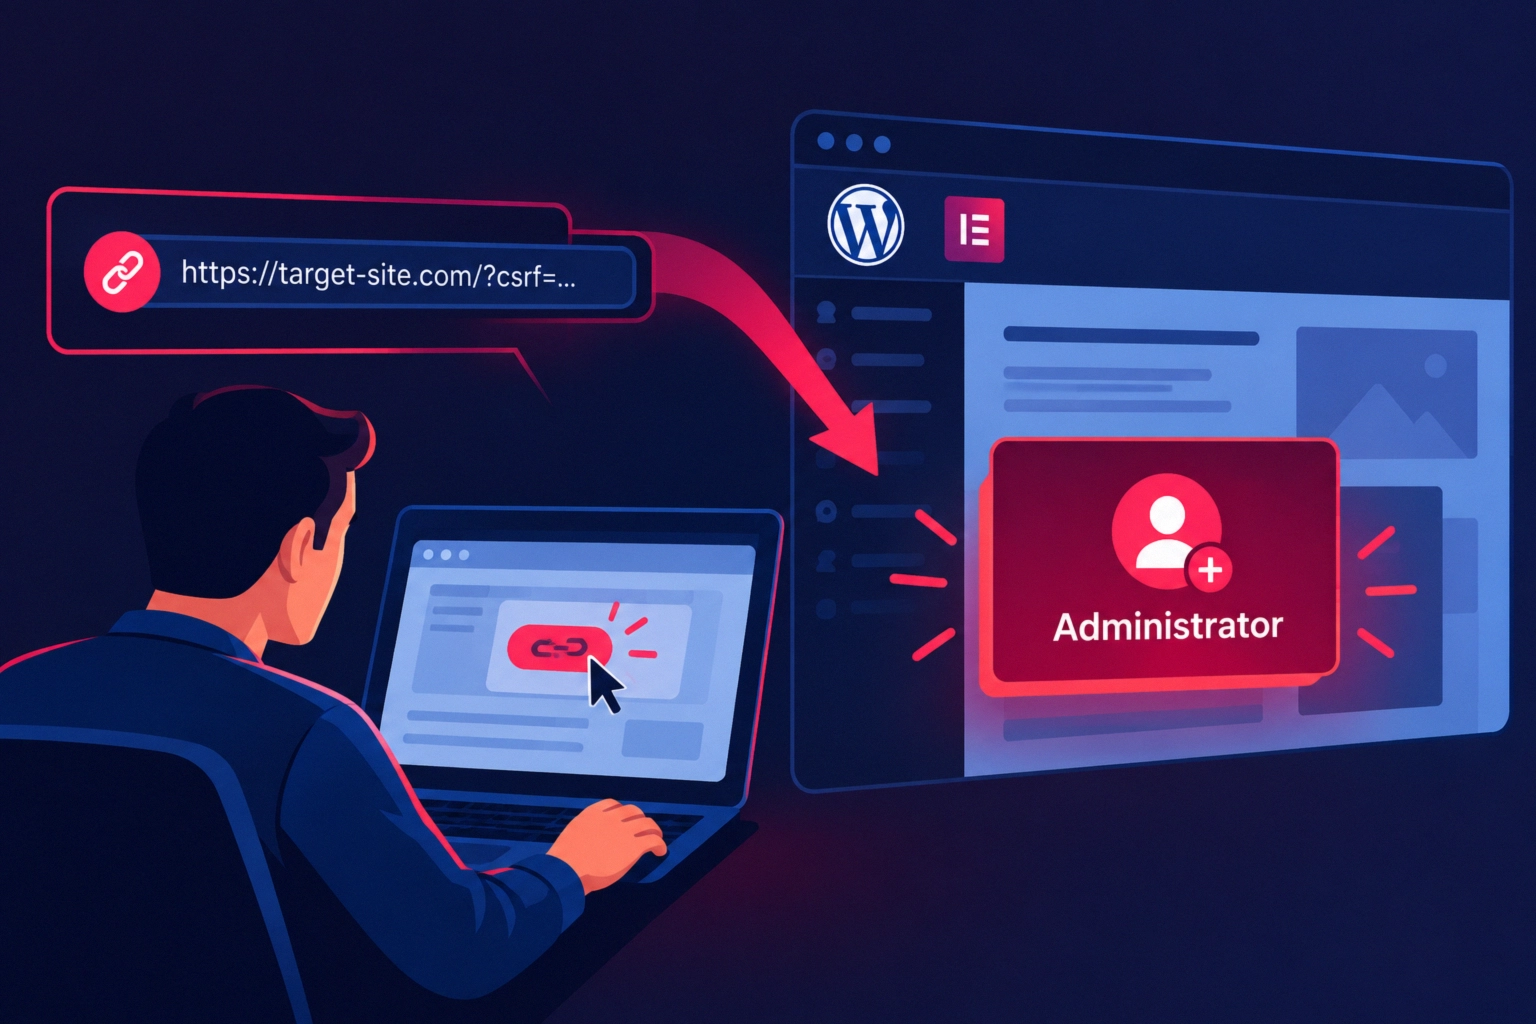
Elementor CSRF vulnerability in WordPress plugin lets attackers create an admin with a single link click
A Elementor Website Builder plugin for WordPress has been found to contain a CSRF (cross-site request forgery) vulnerability which, according ...
watchTowr reports two unpatched remote code execution vulnerabilities in Citrix NetScaler — Citrix remains silent
On 26 September 2026, watchTowr reported two alleged unpatched remote code execution (RCE) vulnerabilities in Citrix NetScaler ADC and NetScaler ...
CISA warns of active exploitation of two critical vulnerabilities in Citrix NetScaler ADC and Gateway
On September 27, 2026, CISA added two critical vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway — CVE-2026-88771 and CVE-2026-88772, ...
CISA added WSO2 and Adobe Commerce vulnerabilities to the Known Exploited Vulnerabilities catalog — what is known and what raises questions
On September 24, 2026, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added two critical vulnerabilities to its Known Exploited ...
CVE-2026-94127: critical F5 BIG-IP APM vulnerability exploited for remote code execution on OAuth servers
F5 has reported active exploitation of a critical vulnerability, CVE-2026-94127, in the BIG-IP Access Policy Manager (APM) module that allows ...
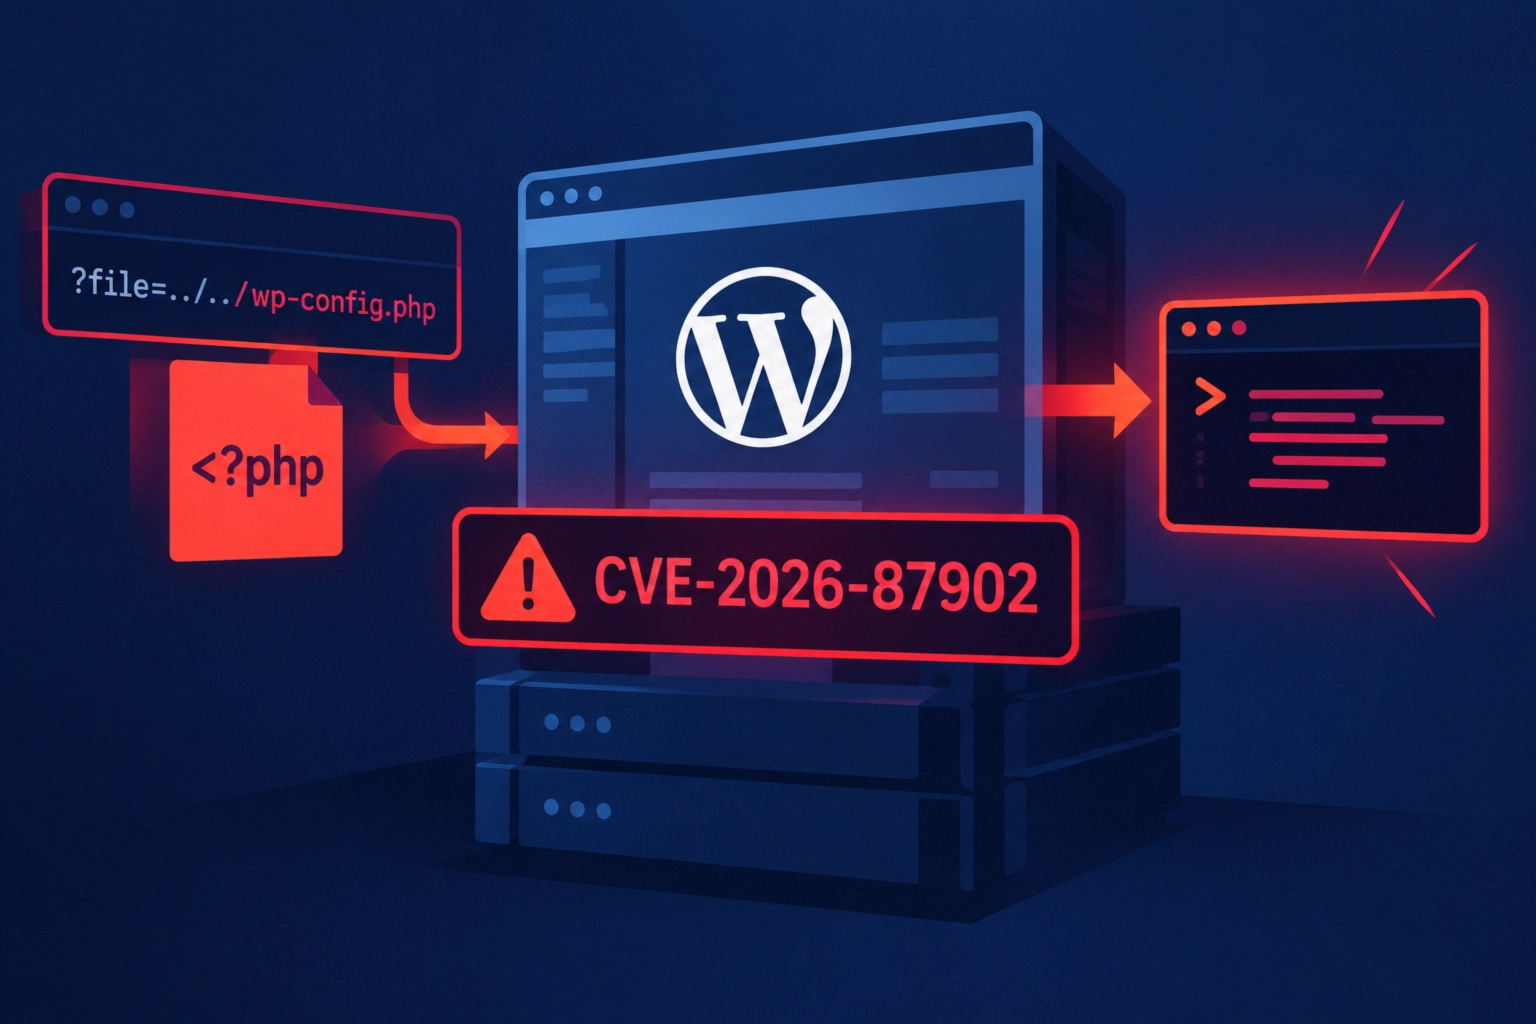
CVE-2026-87902: local file inclusion vulnerability in WordPress — who is affected and how to stay protected
On September 22, 2026, WordPress released the emergency update 7.1.2, which fixes the critical vulnerability CVE-2026-87902 (CVSS 9.2) in the ...
ShinyHunters claims it hacked the FBI: what has been confirmed and what remains just hacker claims
On September 22, 2026, the ShinyHunters group claimed it had compromised systems of the U.S. Federal Bureau of Investigation (FBI) ...