Cybersecurity News
Stay informed about the latest cybersecurity incidents, vulnerabilities, and threat landscape changes. We cover data breaches, ransomware campaigns, critical CVEs, and regulatory updates – with context on what it means for you and how to protect yourself.

Active Exploitation of NGINX CVE-2026-42945 and openDCIM Flaws
The critical vulnerability CVE-2026-42945 in NGINX Plus and NGINX Open, which allows an attacker to cause denial of service or, ...
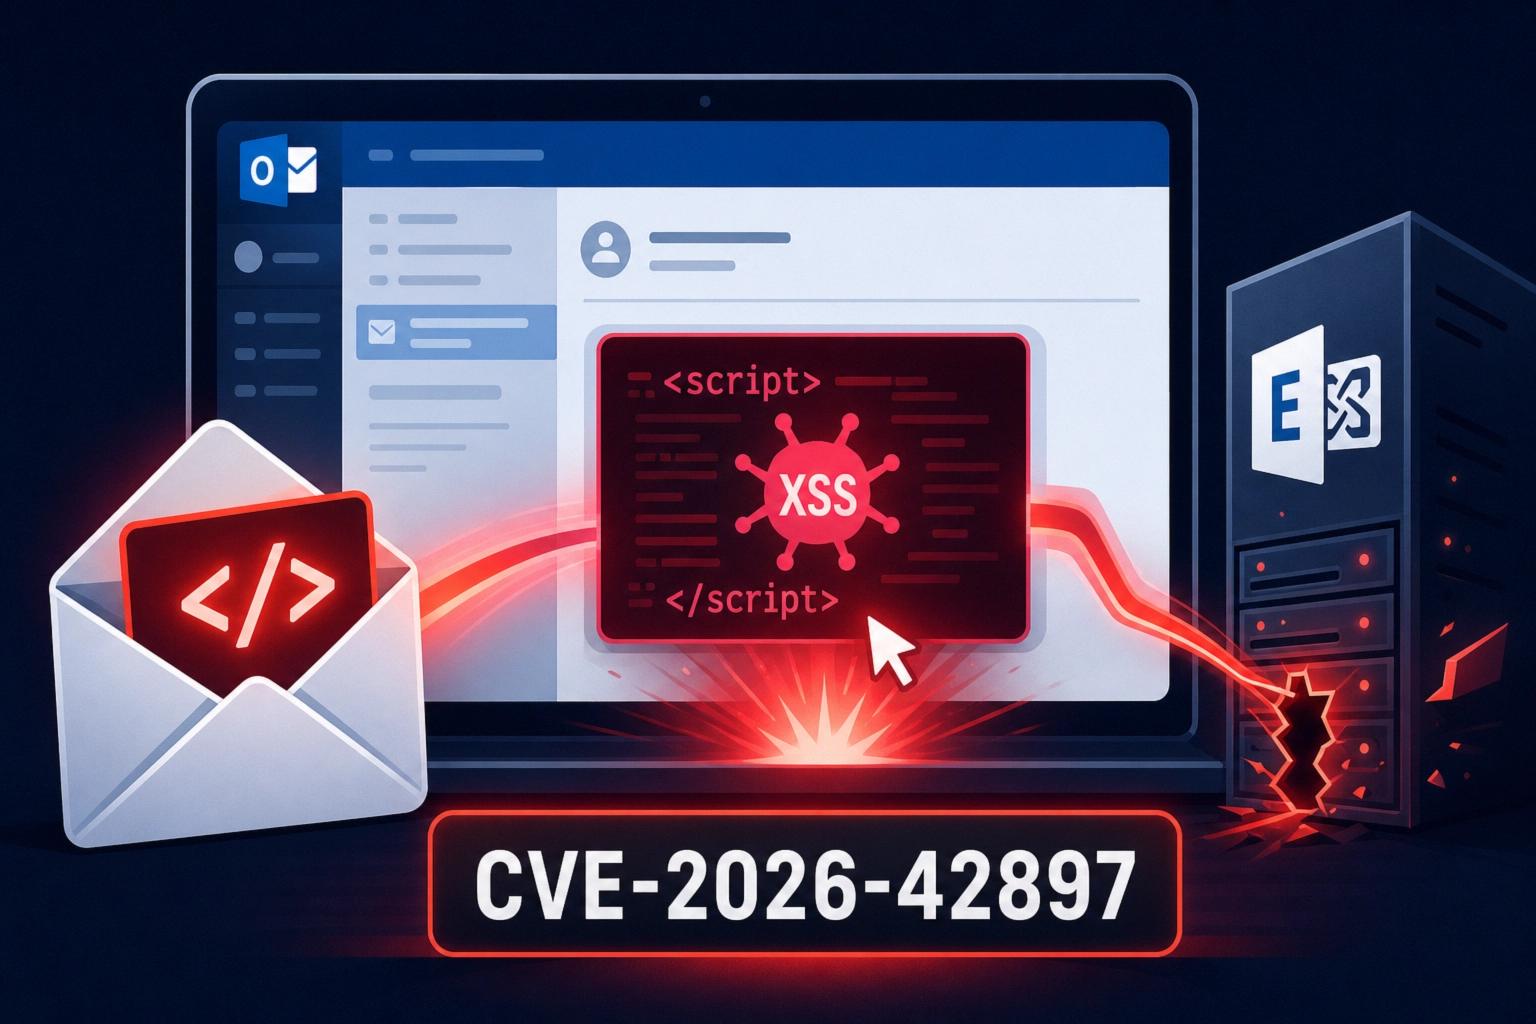
How CVE-2026-42897 Puts On-Premises Exchange Servers at Risk
Microsoft has disclosed vulnerability CVE-2026-42897 (CVSS 8.1) in on-premises versions of Exchange Server, which is already being actively exploited by ...
Urgent Cisco Catalyst SD-WAN Patching for CVE-2026-20182
On 14 May 2026, CISA added the vulnerability CVE-2026-20182 to the Known Exploited Vulnerabilities (KEV) catalog, setting a remediation deadline ...
CVE-2026-44338: Authentication Bypass in PraisonAI API
The critical authentication bypass vulnerability CVE-2026-44338 (CVSS 7.3) in the open multi-agent orchestration framework PraisonAI became the target of active ...
Unpatched BitLocker Bypass and Privilege Escalation in Windows
A researcher using the handle Chaotic Eclipse (Nightmare-Eclipse), who previously disclosed three vulnerabilities in Microsoft Defender, has published information on ...
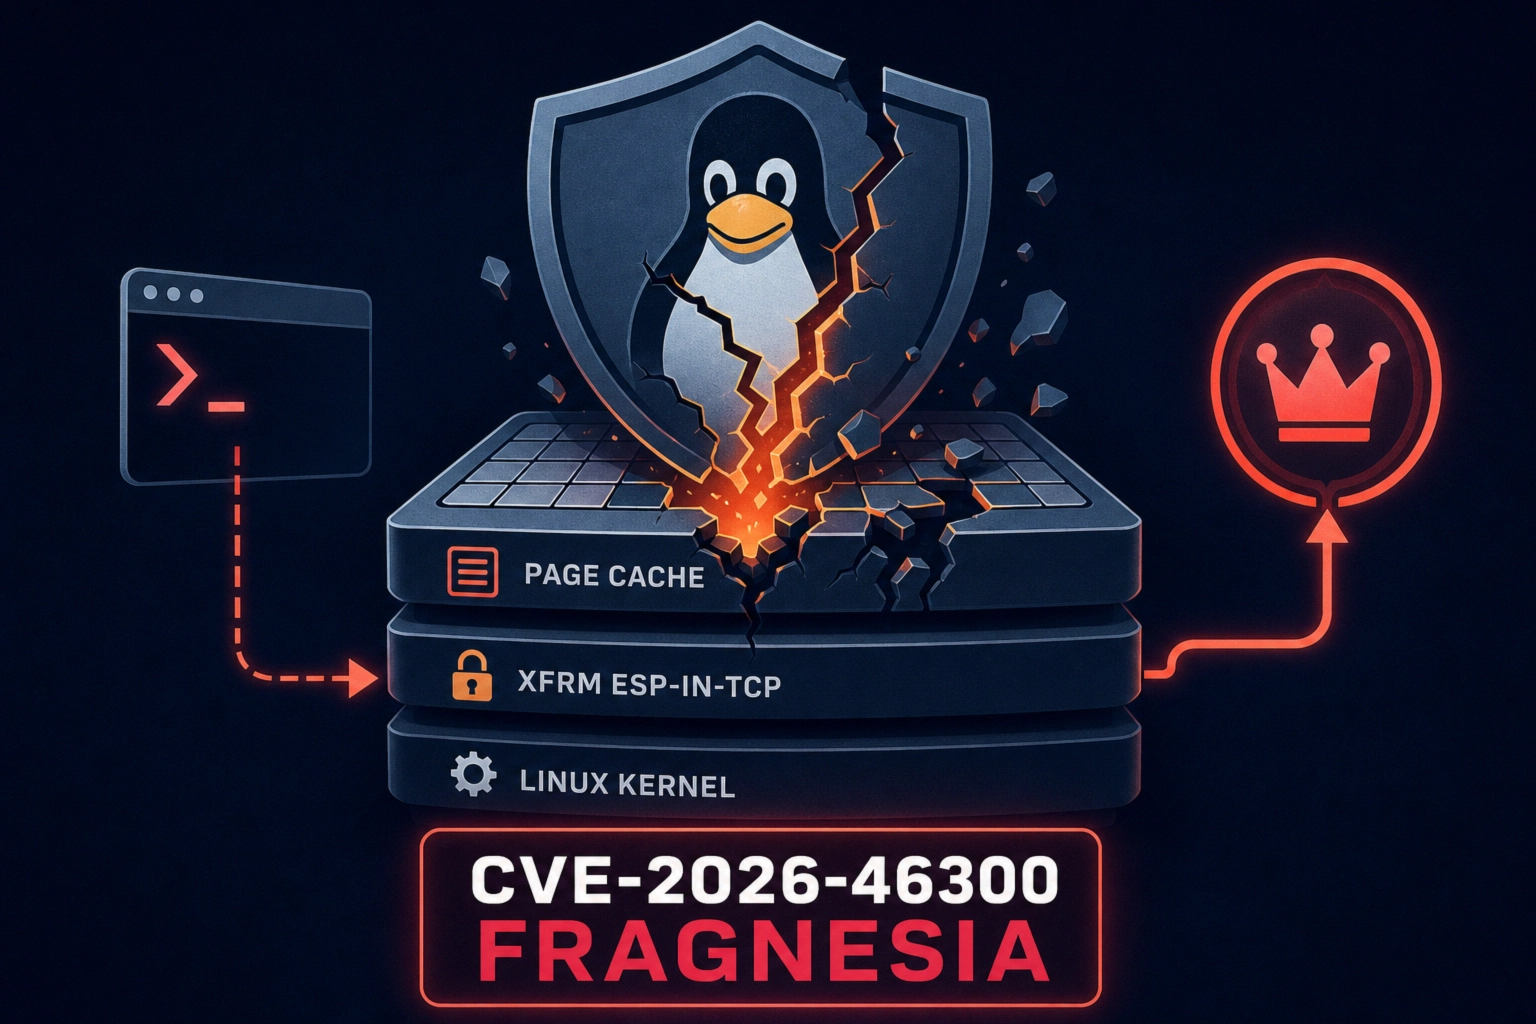
Fragnesia Linux Kernel LPE via ESP-in-TCP (CVE-2026-46300)
The CVE-2026-46300 vulnerability, dubbed Fragnesia, allows an unprivileged local attacker to gain root privileges by corrupting the Linux kernel page ...
Chinese APT Repeatedly Reenters Azerbaijani Oil & Gas Through Exchange
According to Bitdefender researchers, the Chinese cyber-espionage group FamousSparrow carried out a multi-stage operation against an unnamed Azerbaijani oil and ...
Inside MDASH: Microsoft’s Agentic AI for Windows Vulnerability Discovery
Microsoft announced the MDASH (Multi-model Agentic Scanning Harness) system—a multi-model agentic platform for automated detection, validation, and proof of exploitability ...
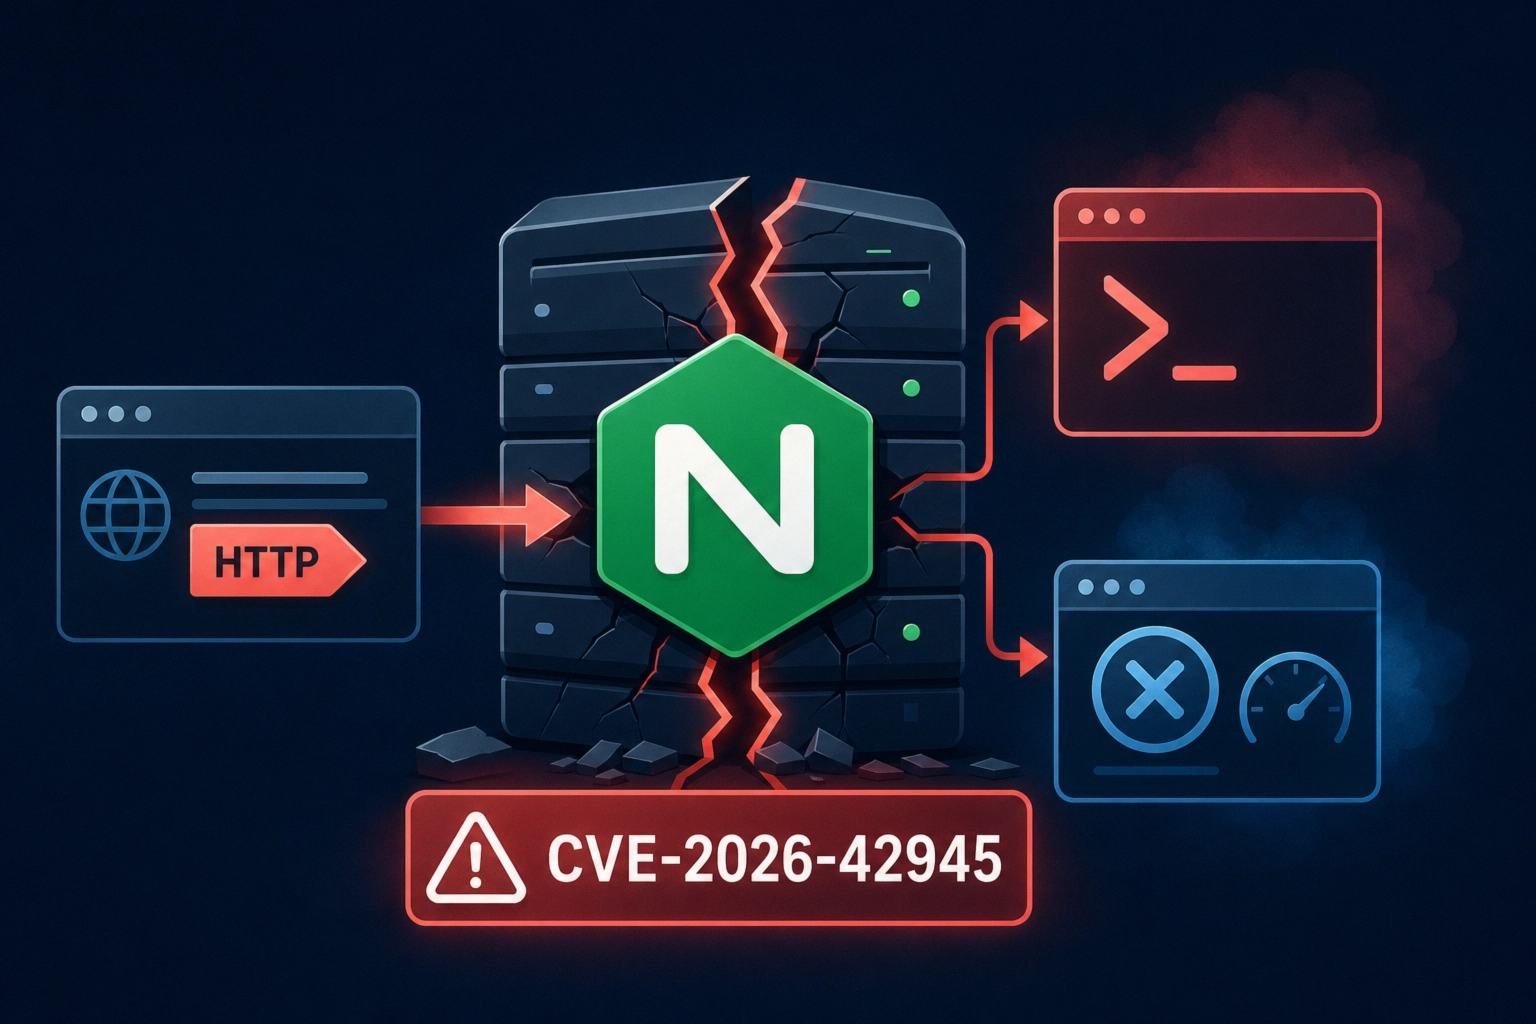
NGINX Rift (CVE-2026-42945): 18-Year Bug Enables RCE
A critical vulnerability CVE-2026-42945 (NGINX Rift, CVSS v4 9.2) has been identified in NGINX Plus and NGINX Open Source, in ...
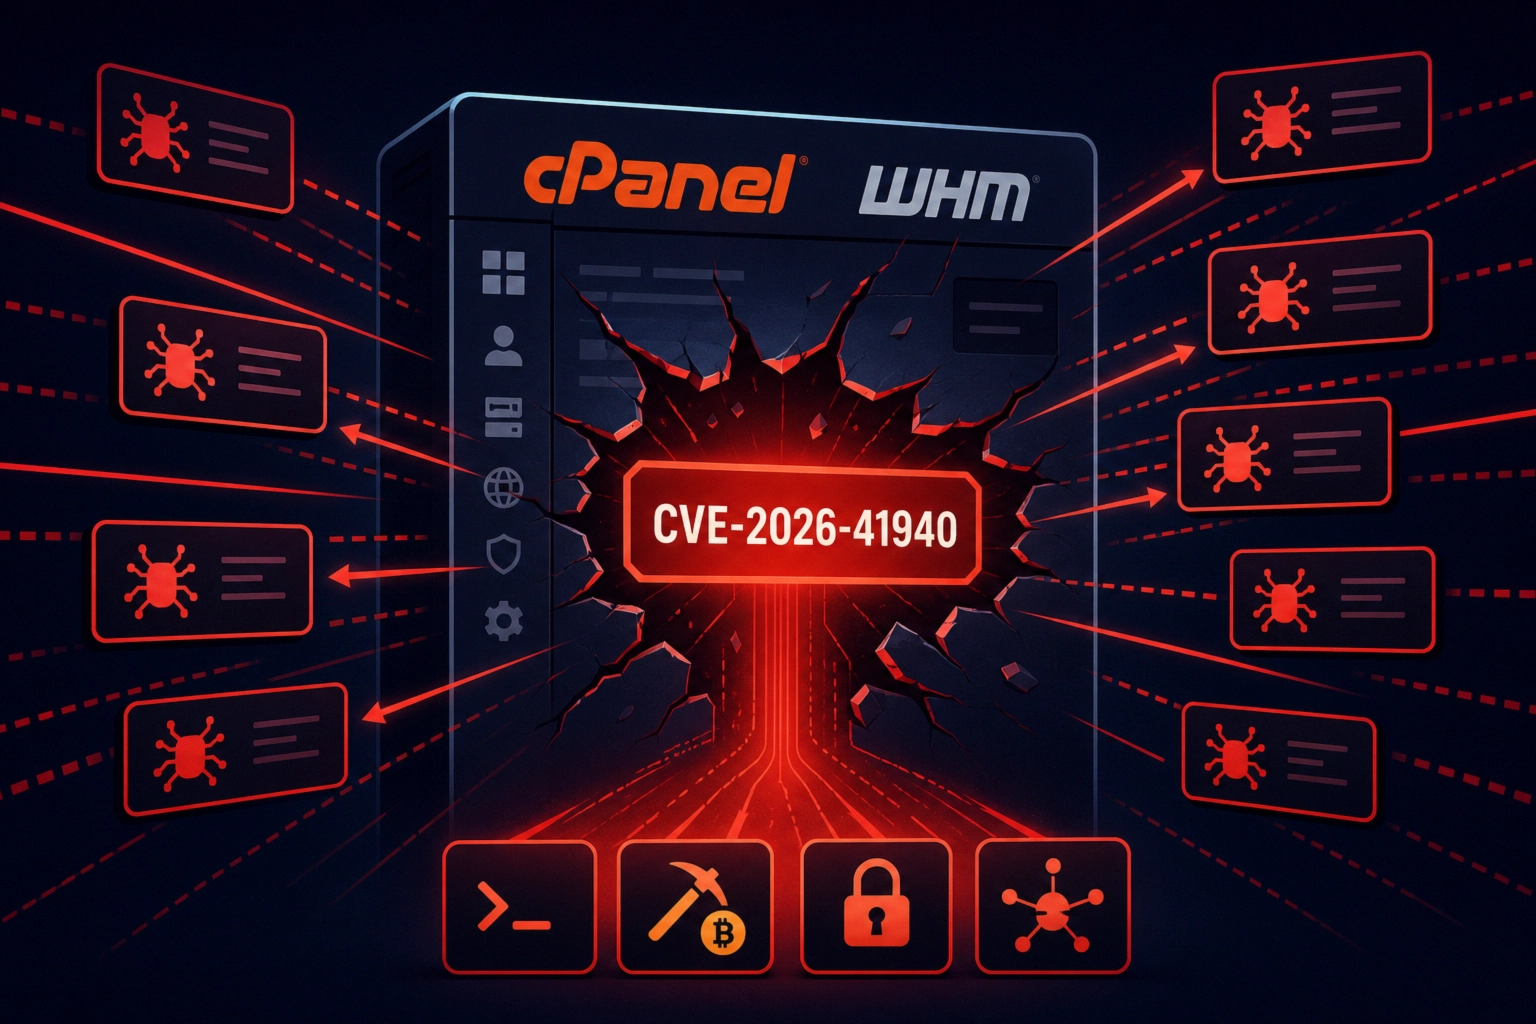
How alleged cPanel CVE-2026-41940 is exploited for backdoors
A critical vulnerability in cPanel and WebHost Manager (WHM), tracked as CVE-2026-41940, is, according to researchers from QiAnXin XLab, being ...