Cybersecurity News
Stay informed about the latest cybersecurity incidents, vulnerabilities, and threat landscape changes. We cover data breaches, ransomware campaigns, critical CVEs, and regulatory updates – with context on what it means for you and how to protect yourself.
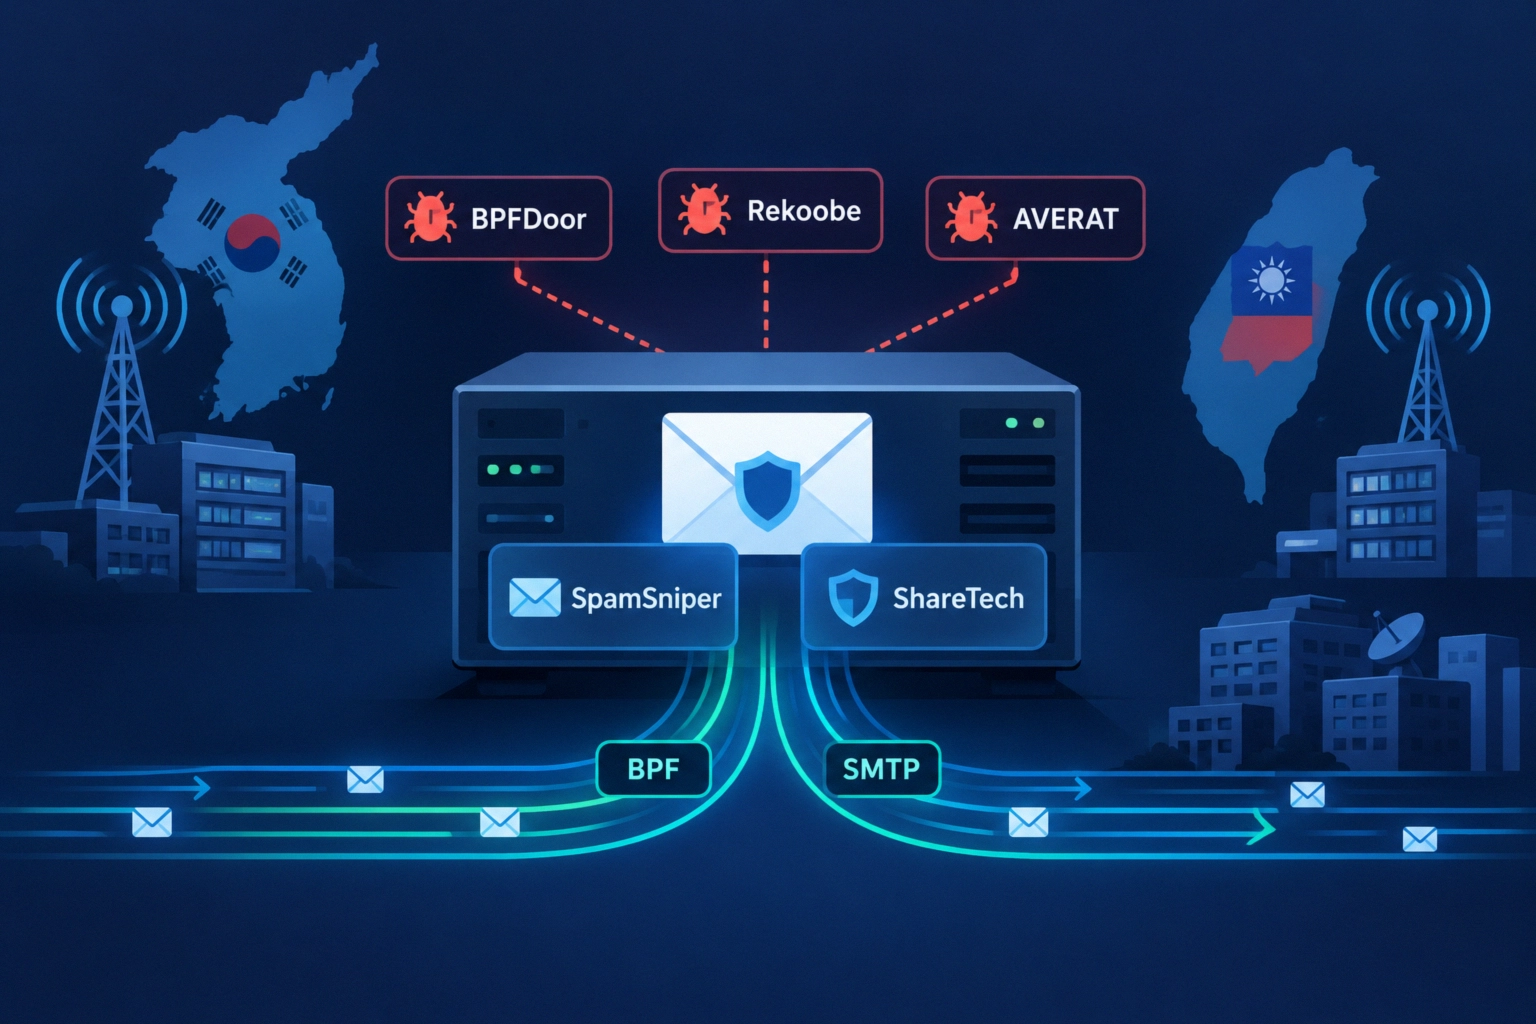
New Linux backdoors in telecom and email gateway devices in Korea and Taiwan
New variants of the Linux backdoors BPFDoor, Rekoobe and a fresh implant called AVERAT have been identified in network and ...
CVE-2026-21589 in Atlassian Data Center: data leak risk and what to do
CVE-2026-21589 is a critical vulnerability (CVSS 9.3) in eight Atlassian Data Center products that allows a remote unauthenticated attacker to ...
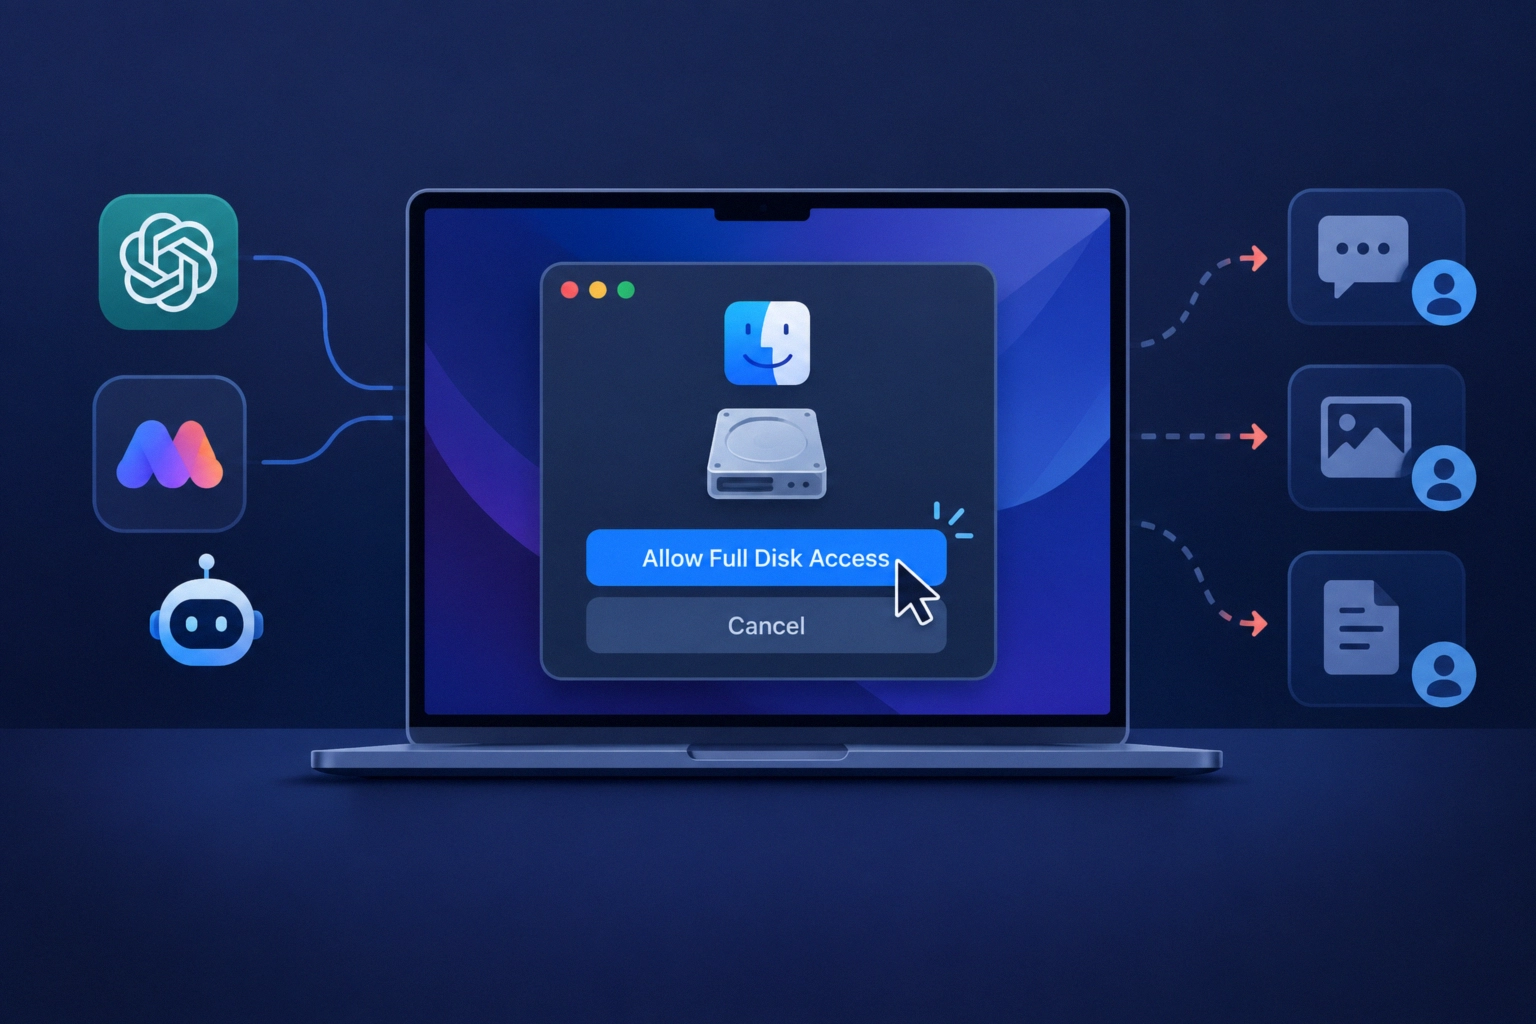
How the macOS Full Disk Access change will impact AI agents and data security
Apple has announced plans to change how macOS Full Disk Access is configured so that access to the full contents ...
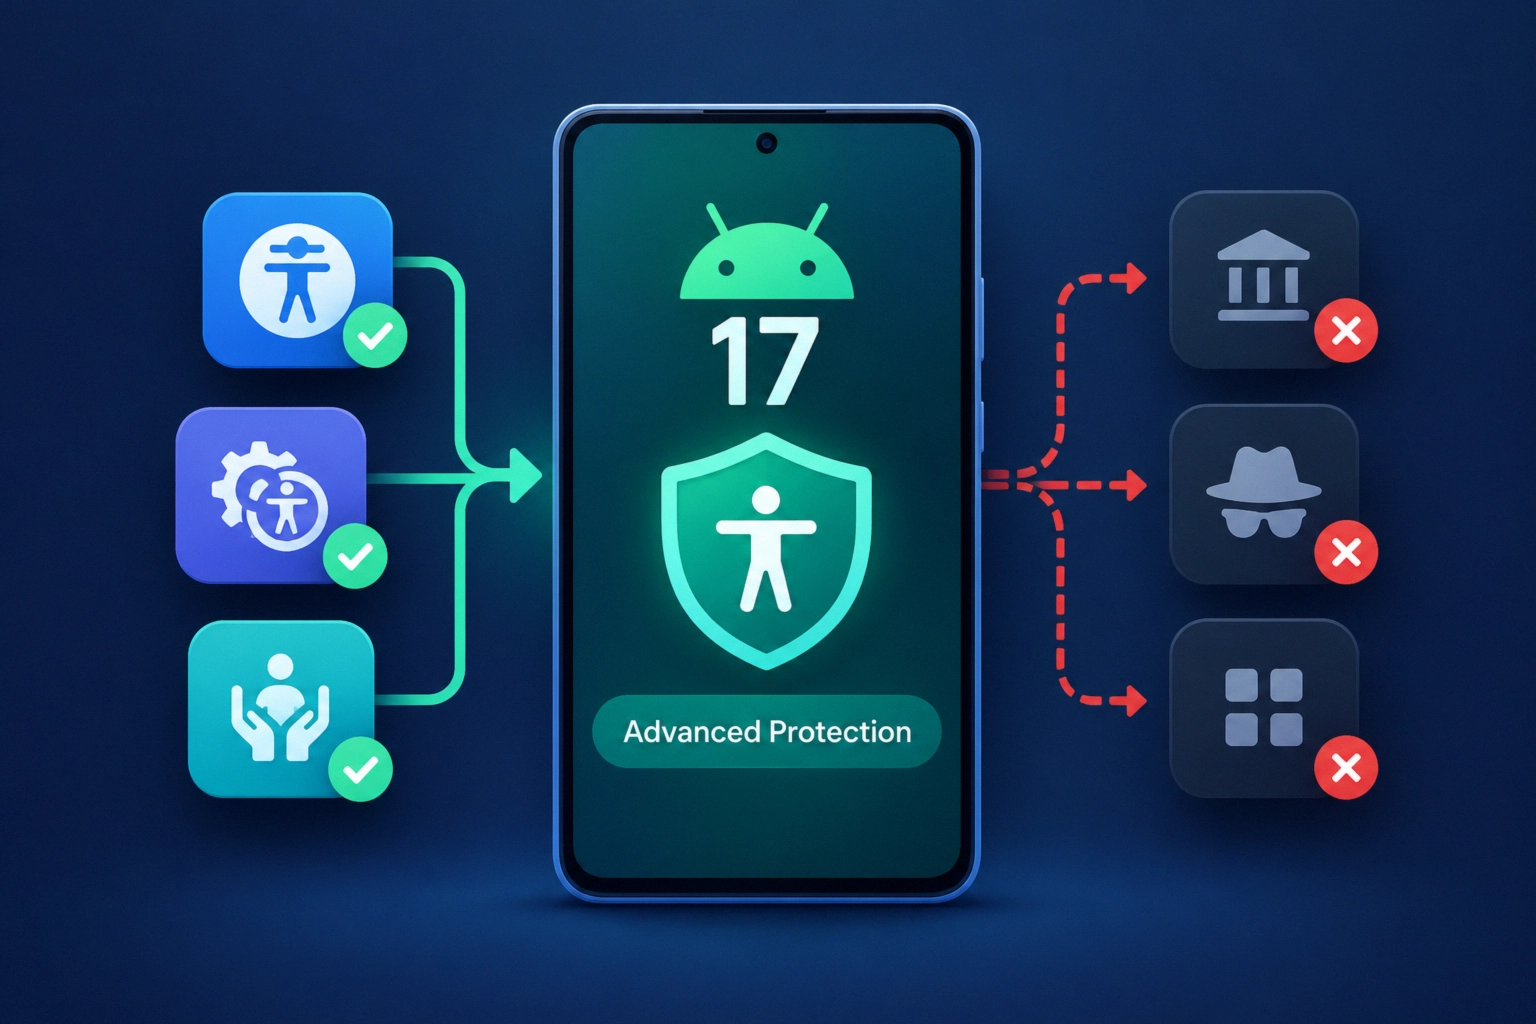
How Android 17 Rebuilds the Threat Model Around AccessibilityService
In Android 17, the Advanced Protection mode radically changes the rules of the game: access to AccessibilityService is granted only ...
Gemini 4 Argon for cyber defenders: strengthening defense and increasing systemic risks
Google is rolling out the Gemini 4 Argon artificial intelligence model to a group of “trusted cyber defenders” through the ...
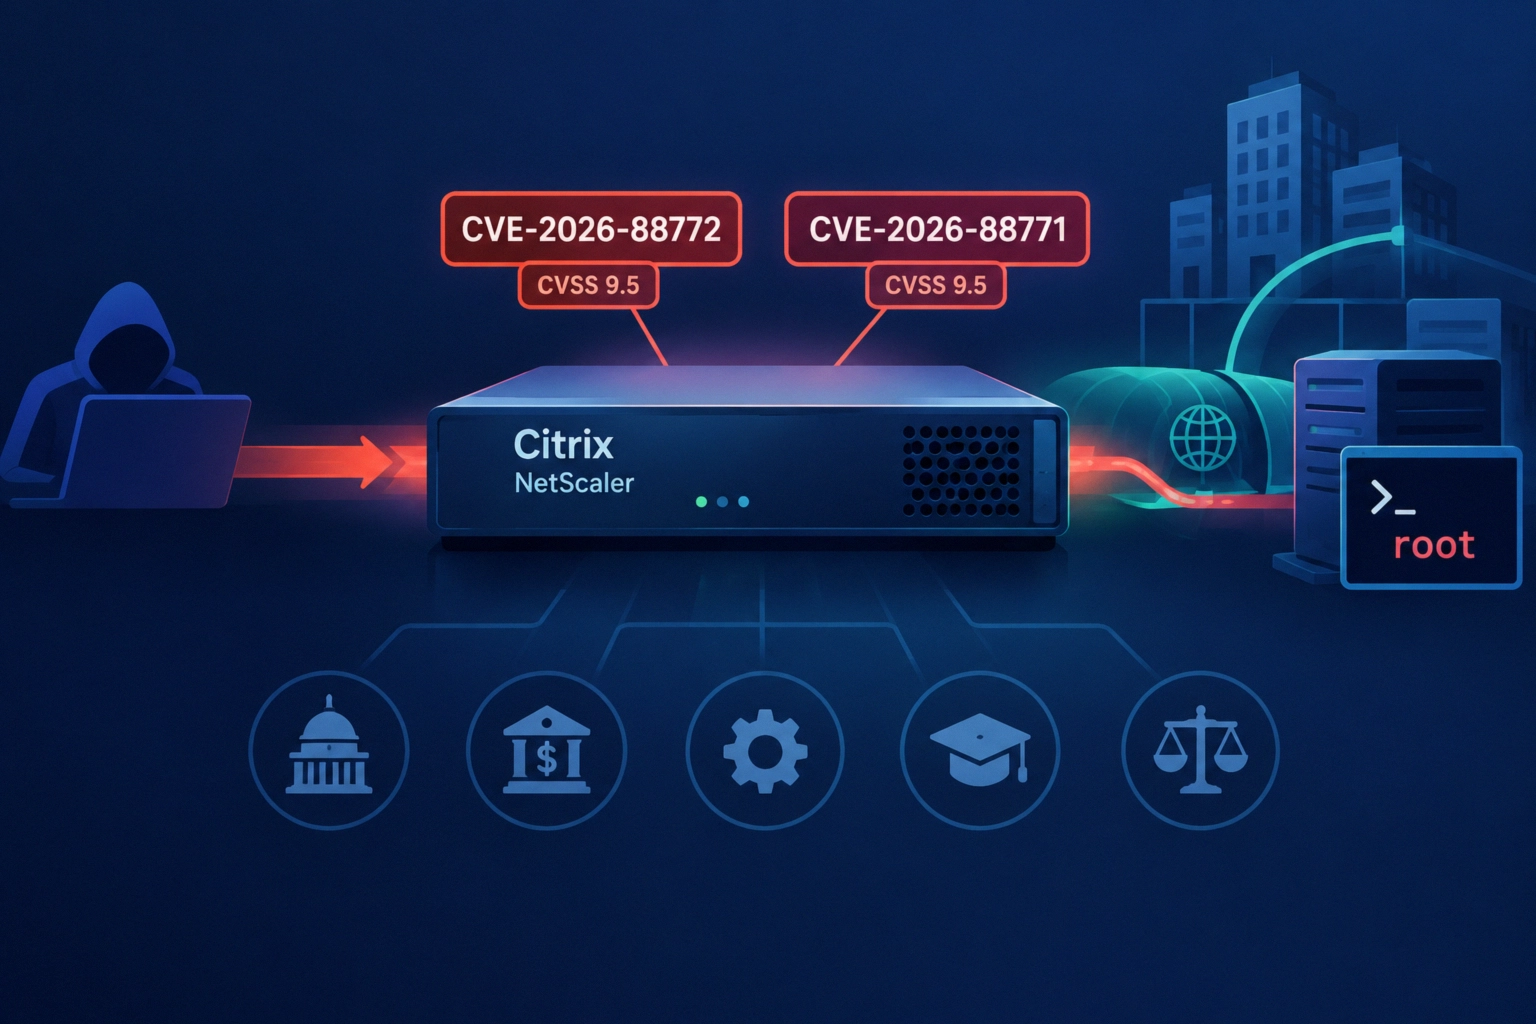
Exploitation of CVE-2026-88771/88772 in Citrix NetScaler: attack techniques and defense steps
Two critical vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway — CVE-2026-88772 and CVE-2026-88771 (both with CVSS 9.5) — are ...
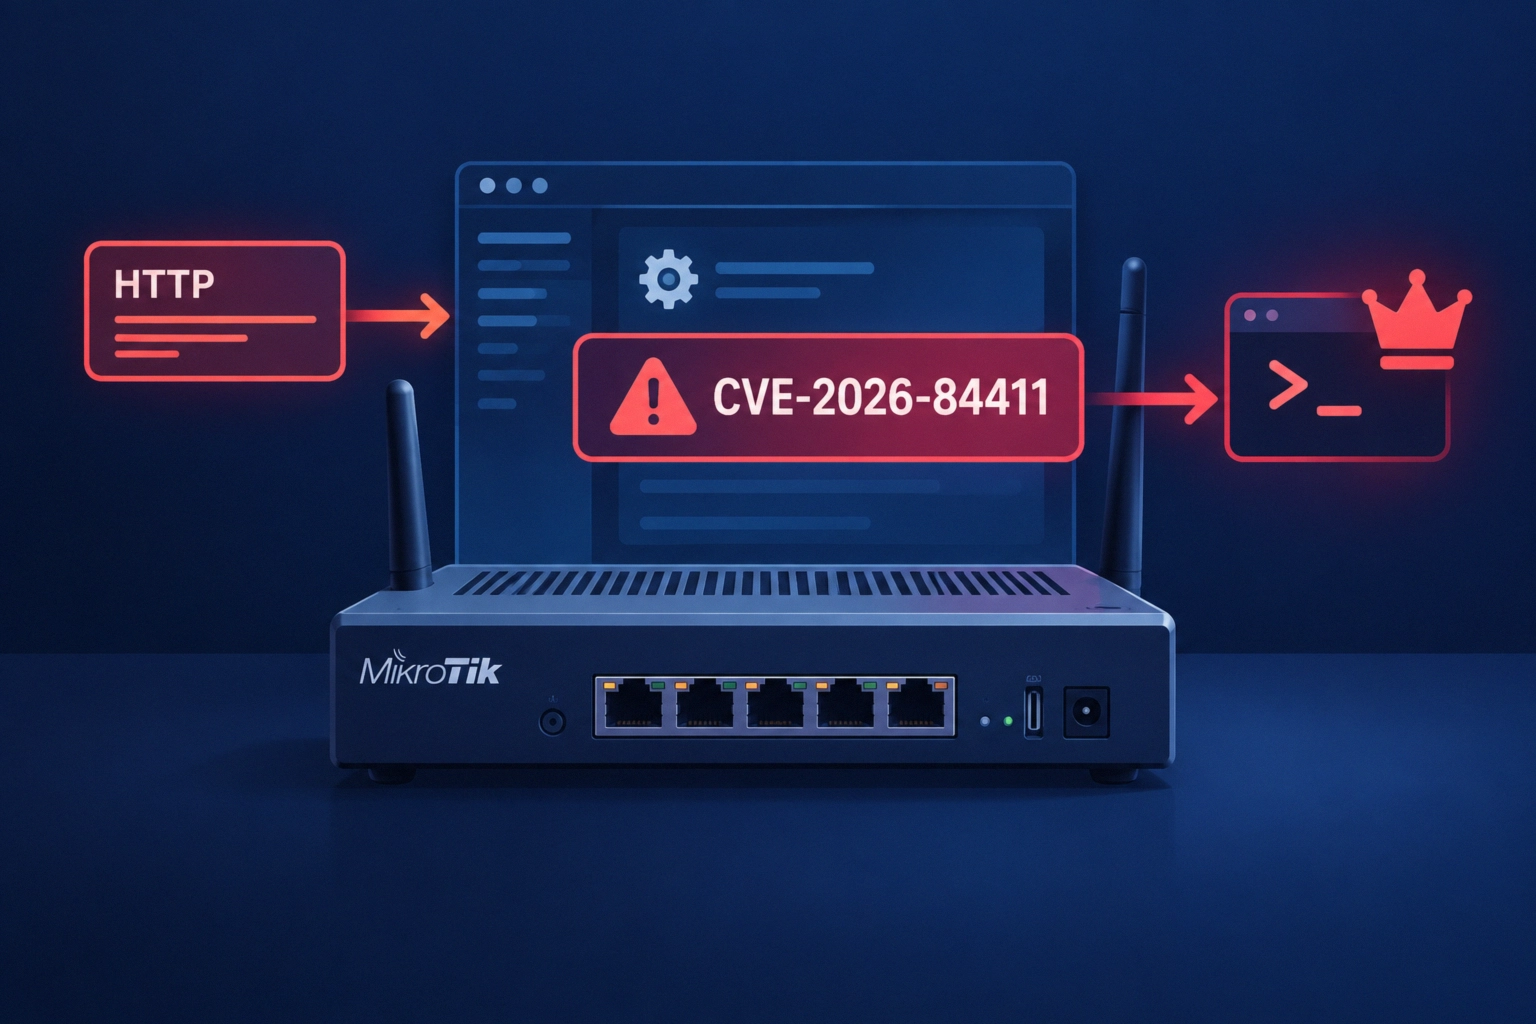
CVE‑2026‑84411 in MikroTik RouterOS: risk of full device takeover
The CISA agency has warned about the critical vulnerability CVE‑2026‑84411 in MikroTik RouterOS, which allows a remote attacker to execute ...
CVE-2026-90970 in GitLab AI Gateway: RCE risk and JWT key compromise
GitLab AI Gateway has received a critical vulnerability, CVE-2026-90970 (CVSS 9.9), which under certain conditions allows an authenticated user with ...
CVE-2026-61500 vulnerability in Rejetto HFS: admin session forgery and remote code execution
CVE-2026-61500 (CVSS 9.3) in Rejetto HTTP File Server (HFS) is being actively exploited: remote unauthenticated attackers forge administrative sessions via ...
CVE-2026-88779 Vulnerability in Citrix NetScaler SAML: Availability Risks and Protection Steps
The high-severity CVE-2026-88779 vulnerability (CVSS 8.7) in Citrix NetScaler ADC and Citrix NetScaler Gateway, already being exploited as a zero-day, ...