Cybersecurity News
Stay informed about the latest cybersecurity incidents, vulnerabilities, and threat landscape changes. We cover data breaches, ransomware campaigns, critical CVEs, and regulatory updates – with context on what it means for you and how to protect yourself.
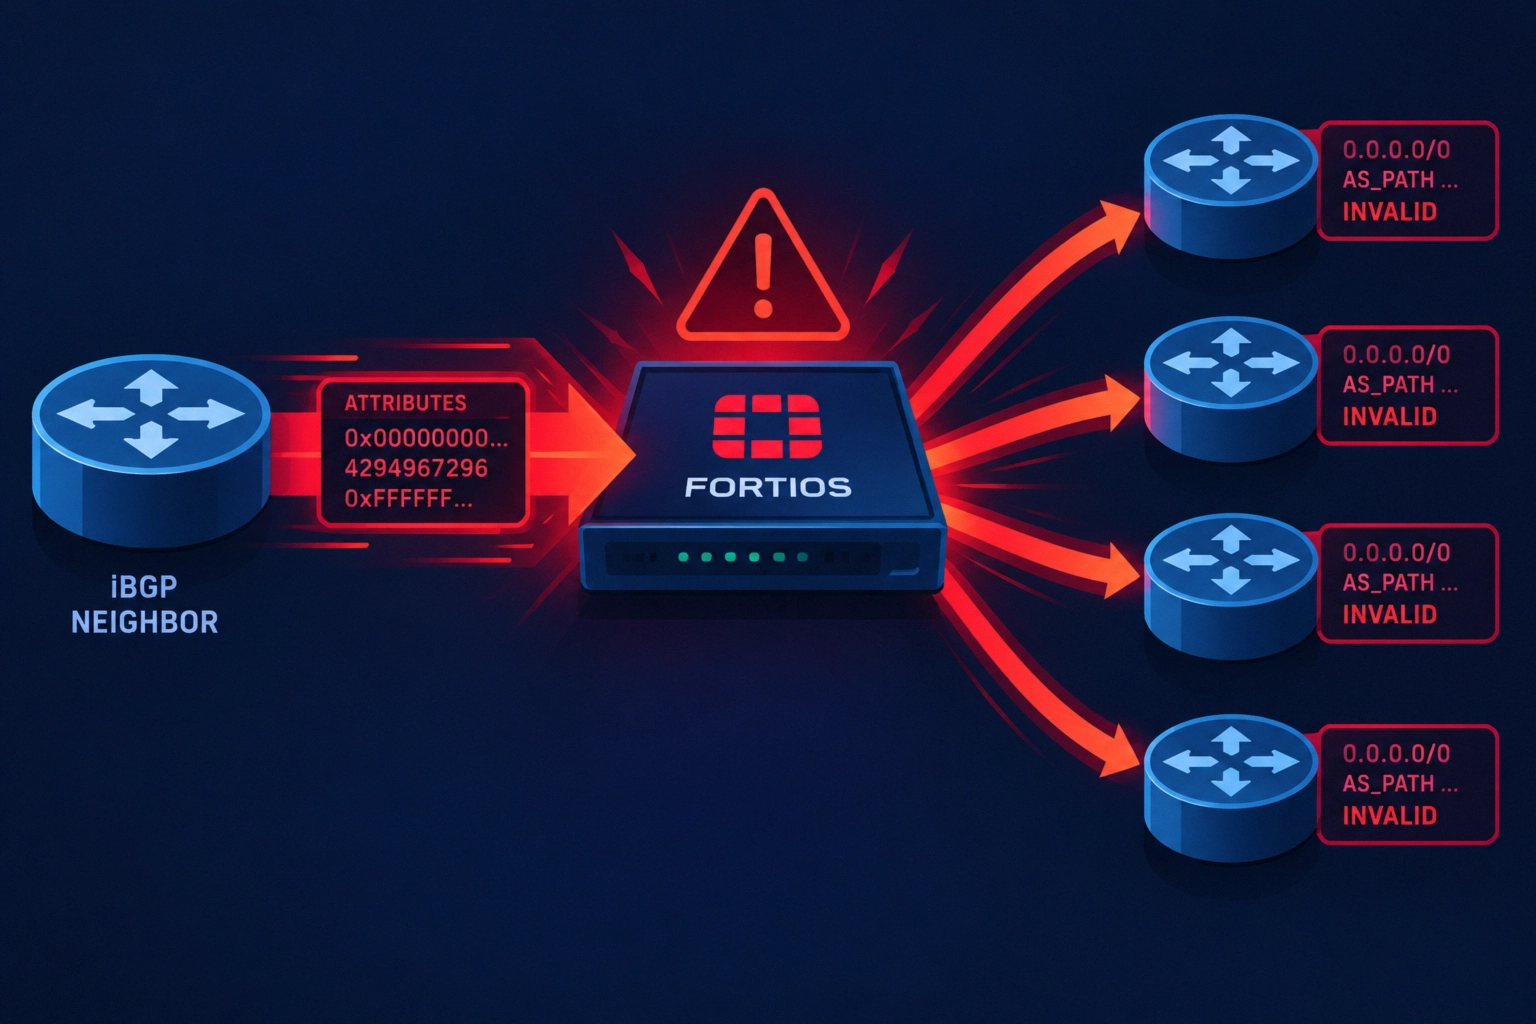
CVE-2026-126254: numeric truncation vulnerability in the FortiOS and FortiSASE BGP daemon (CVSS 9.6)
Fortinet has published security advisory FG-IR-26-268 describing the critical vulnerability CVE-2026-126254 in the BGP daemon of FortiOS and FortiSASE. This ...
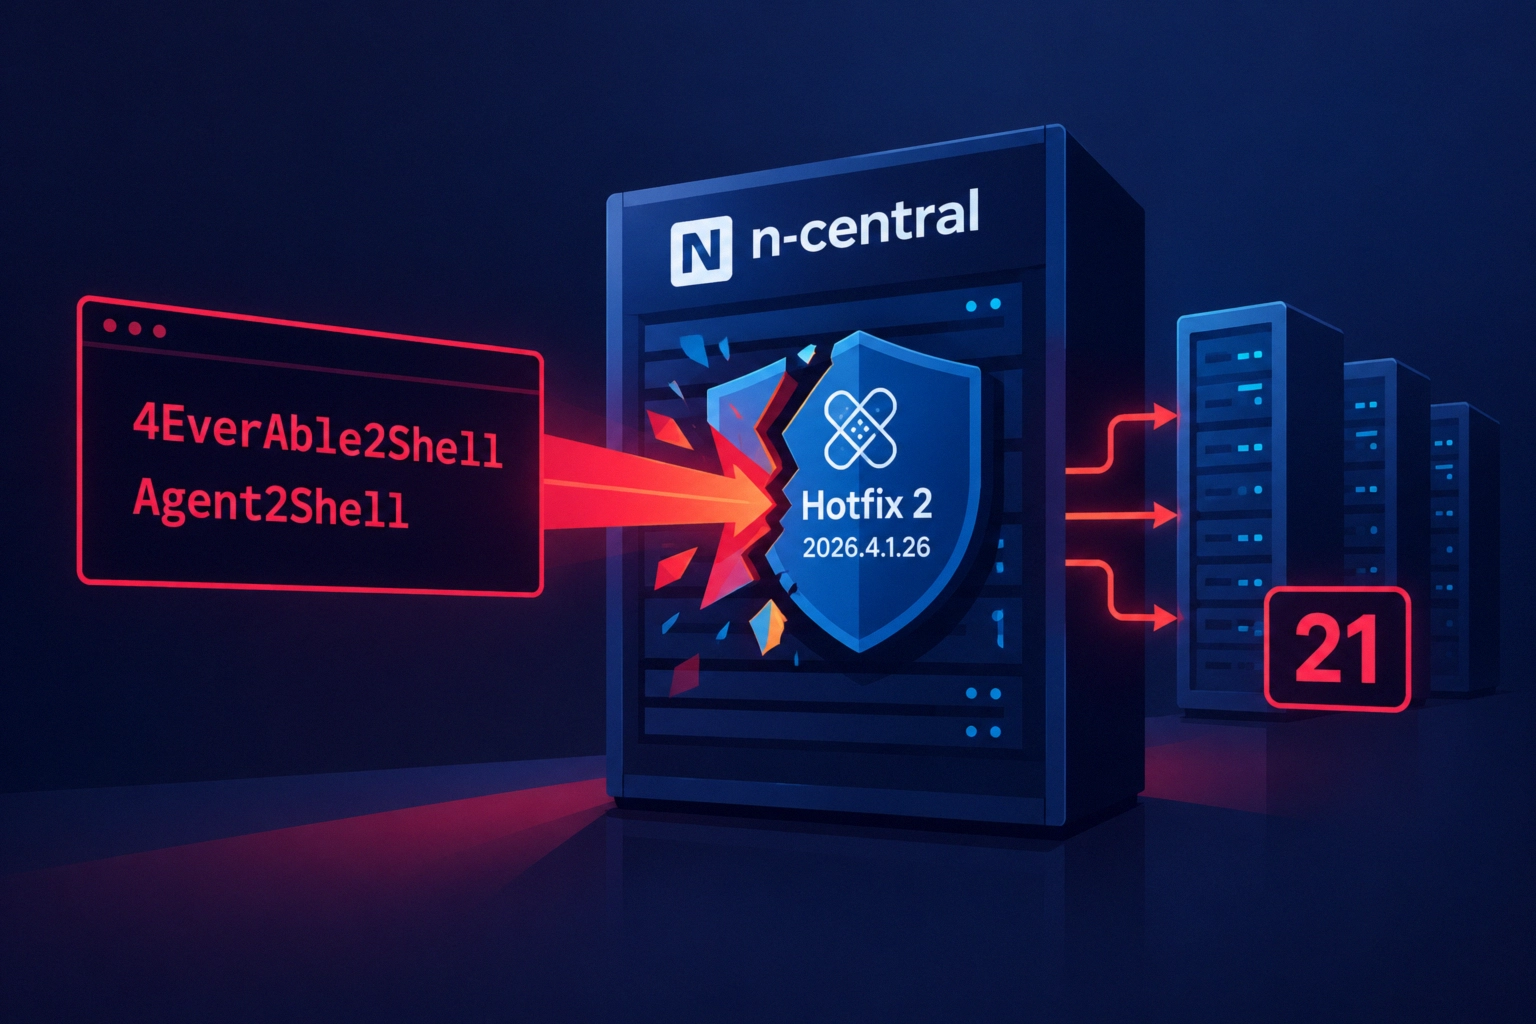
New 4EverAble2Shell and Agent2Shell exploits affect patched N-able N-central servers
Independent security researcher Sean Bales has published new exploits 4EverAble2Shell and Agent2Shell for the N-able N-central remote management platform which, ...
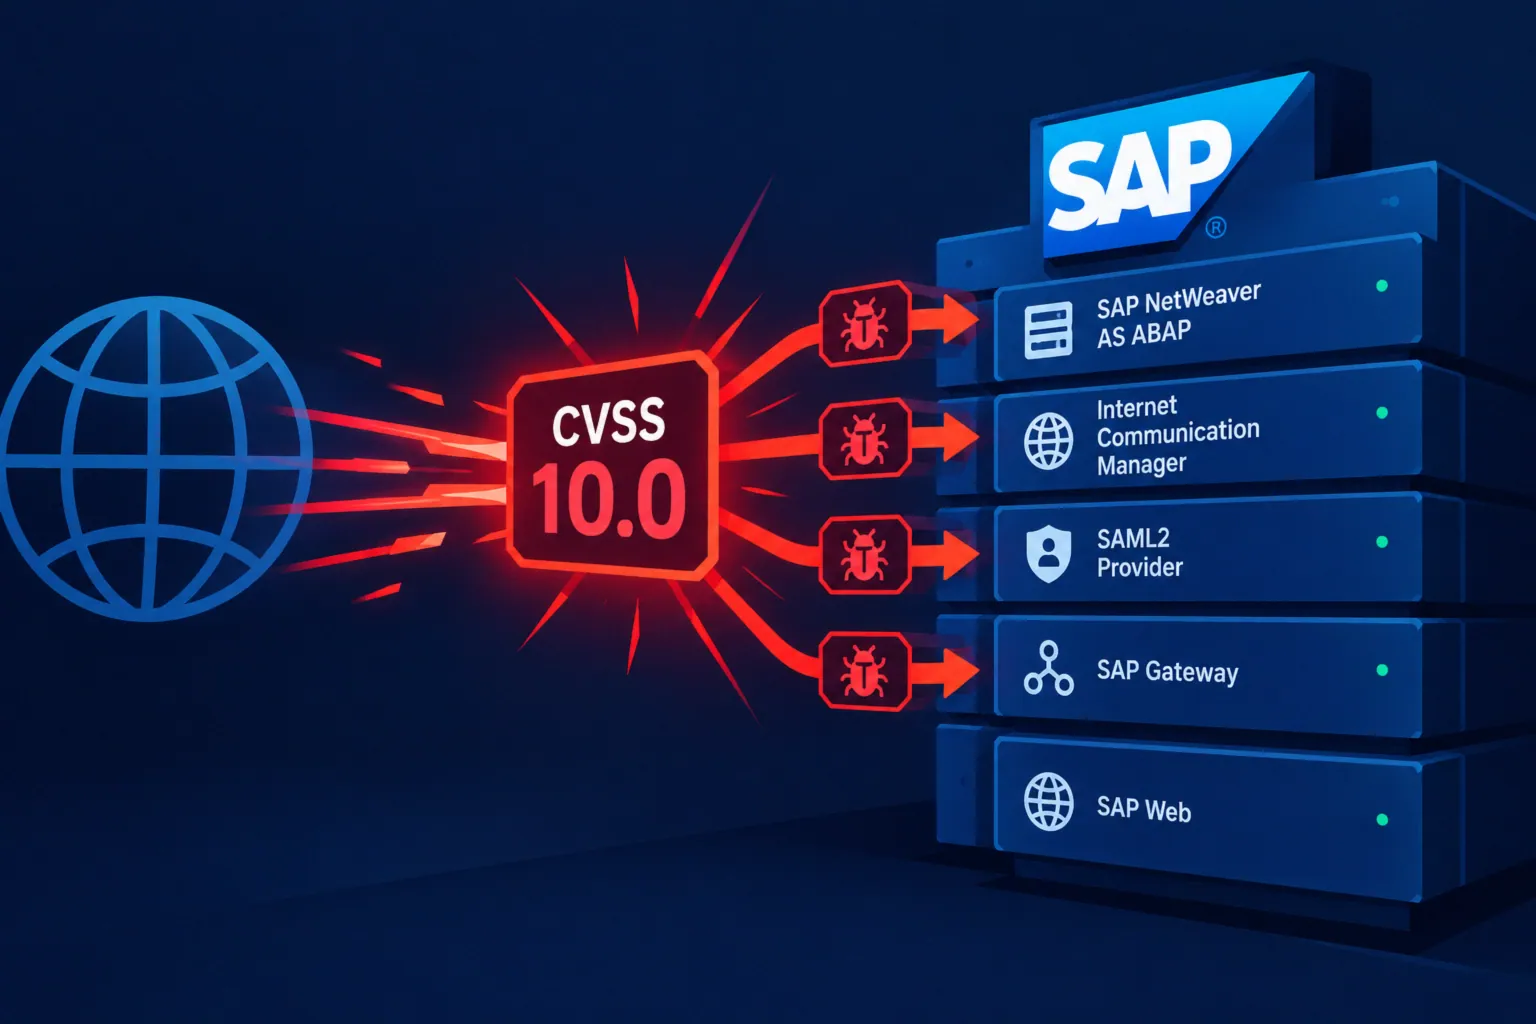
Four critical CVSS 10.0 vulnerabilities in SAP NetWeaver and Web Dispatcher: analysis and recommendations
As part of the November Security Patch Day, SAP released fixes for four vulnerabilities, each of which received the maximum ...
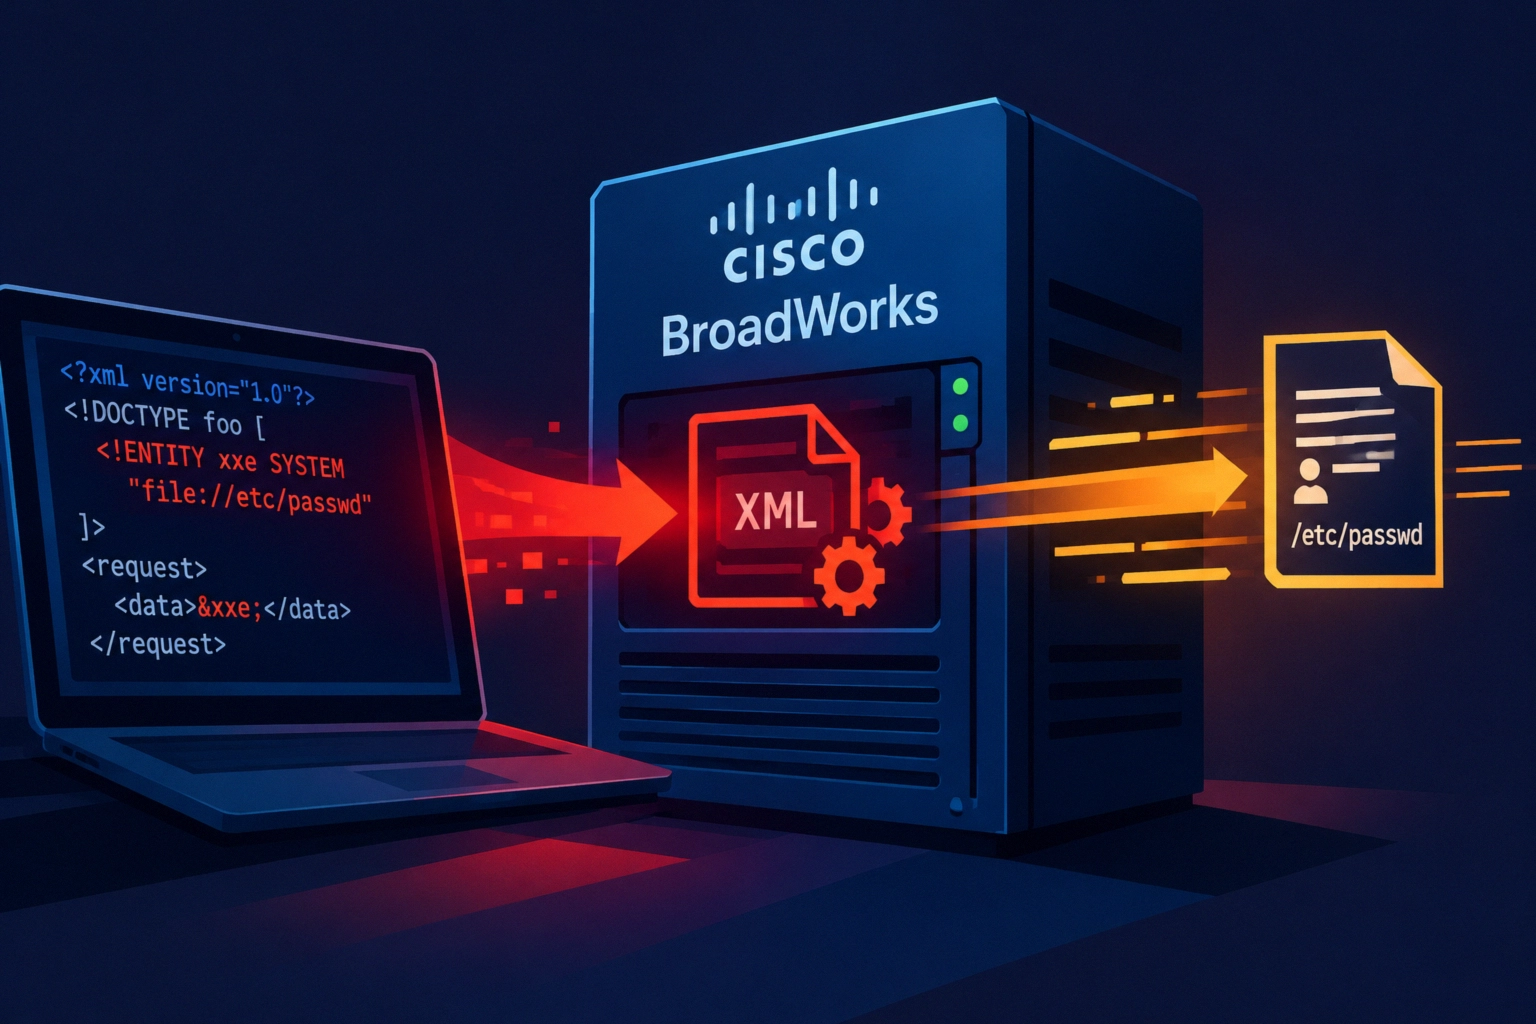
CVE-2026-20320 in Cisco BroadWorks: what is known about the vulnerability and the controversies around its exploitation
The Hacker News reported that CISA had added two vulnerabilities — in Cisco BroadWorks and Openwave Messaging Webtop Media Transcoder ...
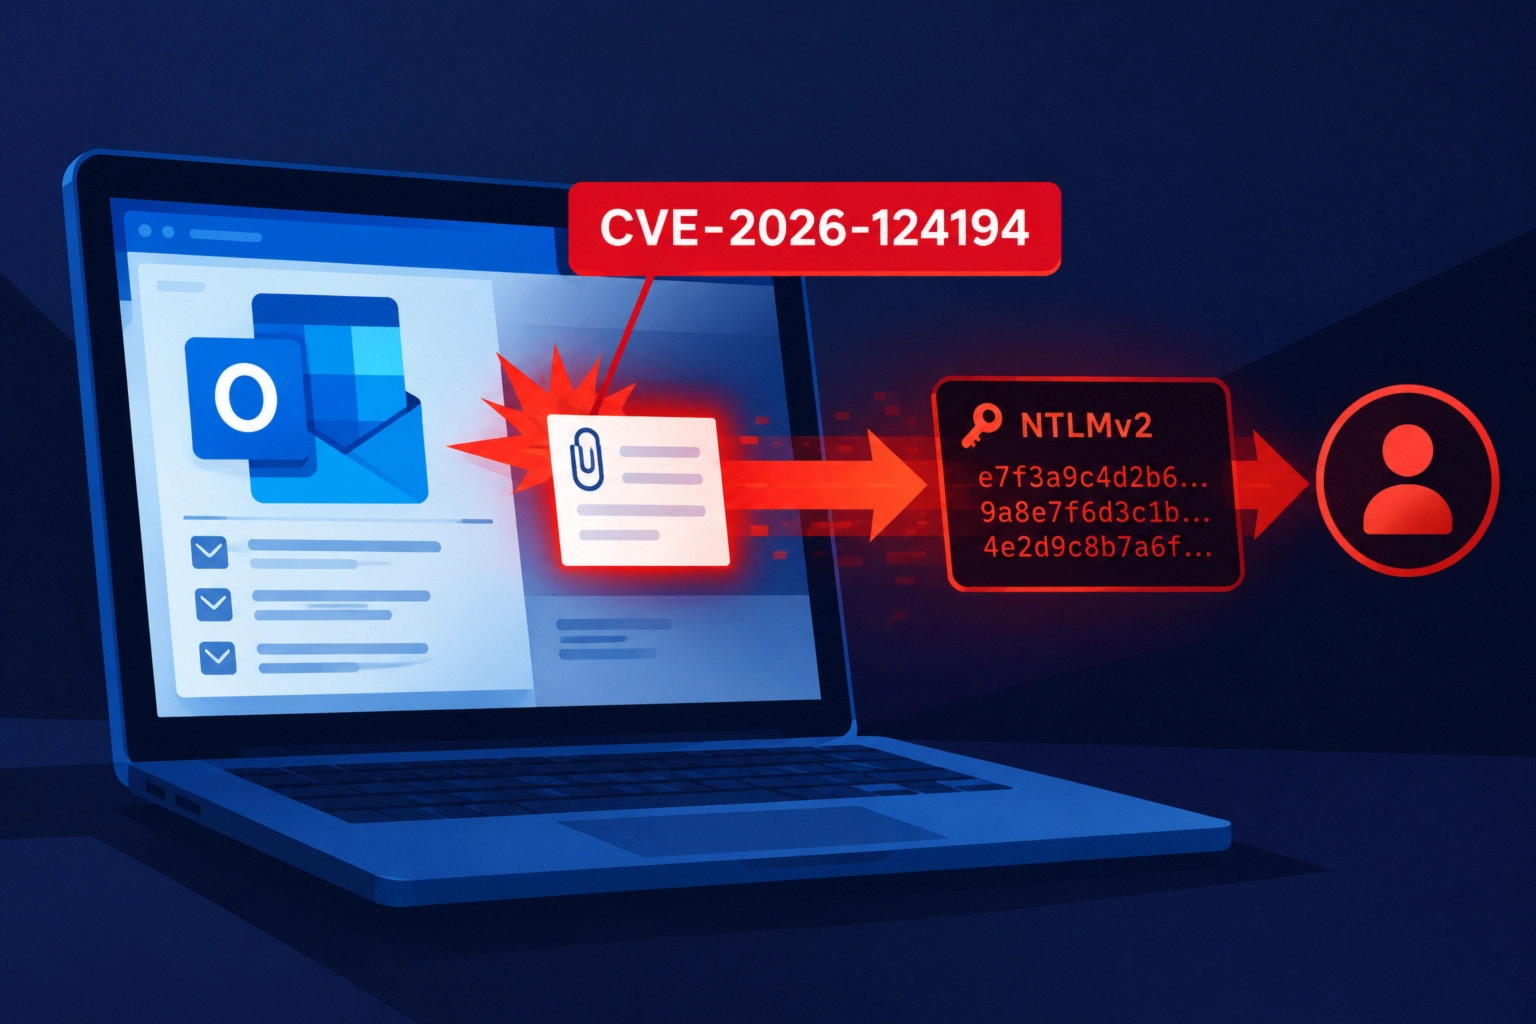
Microsoft patches over a thousand vulnerabilities — Outlook bug leaking NTLMv2 hashes already used by attackers
Microsoft’s November Patch Tuesday is the second consecutive update with more than a thousand fixes. The main threat is the ...
CISA warns of exploitation of OpenSSH, GPUStack, FreeSWITCH and IBM Aspera Faspex vulnerabilities
On November 9, 2026, CISA added four vulnerabilities to the Known Exploited Vulnerabilities (KEV) catalog affecting OpenSSH, GPUStack, SignalWire FreeSWITCH, ...
Google releases emergency Chrome 157 update as XML use-after-free vulnerability is already being exploited
Google has released an update to the stable Chrome channel to versions 157.0.8103.50/.51 for Windows and macOS and 157.0.8103.50 for ...
CVE-2026-124194 — Microsoft Outlook spoofing vulnerability with confirmed exploitation
Microsoft reports active exploitation of vulnerability CVE-2026-124194 in Microsoft Office Outlook. The issue belongs to the spoofing class: the product ...
Unpatched vulnerability in CryptoPayment Gateway WordPress plugin exposes wallet credentials
The critical vulnerability CVE-2026-81648 with a CVSS 10.0 score has been discovered in the CryptoPayment Gateway WordPress plugin versions 1.2.1 ...